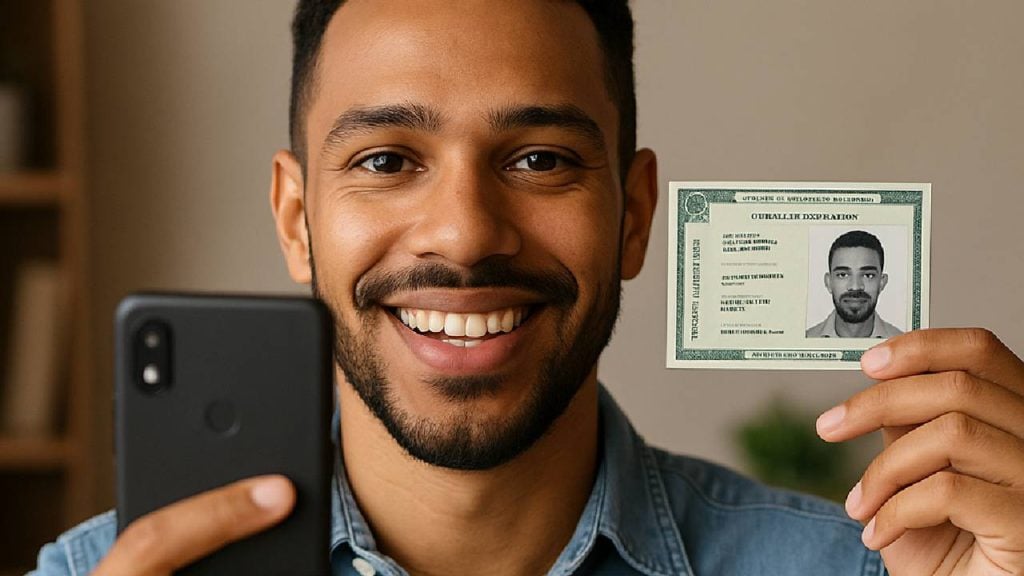
Selfie with document It is a way to add evidence of identity to registrations, validations, and processes. electronic signatureDepending on the solution, the selfie and the document may simply be registered, undergo facial comparison, receive proof of life verification, or be integrated into a more complete identity validation. Therefore, sending both images does not automatically mean that the document has been authenticated or that the identity has been confirmed.
Summary
- Selfie, facial recognition, proof of life, and identity validation are different mechanisms.
- A simple photo can serve only as visual evidence, without automatic biometric comparison.
- Good lighting, framing, and sharpness help both human analysis and facial recognition systems.
- Biometric data used to identify a person are considered sensitive personal data under the LGPD (Brazilian General Data Protection Law).
- Companies should choose the level of verification based on risk, purpose, and user experience.
Quick facts
- Biometrics receive special protection: a General Law of Data Protection biometric data linked to a natural person is considered sensitive.
- Consent is not the only option: a guidance from ANPD Remember that sensitive personal data must be supported by one of the legal grounds provided for in Article 11 of the LGPD (Brazilian General Data Protection Law).
- Facial recognition has limitations: o ANPD Technological Radar It warns of the risks of errors, privacy concerns, and potential discriminatory effects in biometric systems.
- Capture quality influences the result: current assessments of NIST FRTE program They point out that inadequate lighting and photo quality can increase facial matching errors.
- Biometrics remains on the regulatory agenda: a current agenda of the ANPD The discussion regarding parameters for the processing of biometric data remains ongoing.
- Deepfakes increase the challenge: o Radar on deepfakes Published in 2026, it analyzes risks associated with synthetic content and identity manipulation.
What is a selfie with identification?
"Selfie with ID" is a common name for digital processes in which a facial image and an identification document are collected to add evidence about who is performing a particular action.
These images can be captured in the same photo or at separate times. At ZapSign, for example, it's possible to request a selfie and photographs of the document as distinct steps in the workflow.
This difference is important because Collecting two images does not necessarily mean automatically validating them..
A platform can:
- just save the selfie;
- just save the photos of the document;
- Record both in the report;
- Biometrically compare the face with the photograph on the document;
- to check if there is a real person in front of the camera;
- validate registration data;
- Analyze the document's authenticity indicators.
Therefore, before concluding that a solution "validates identity," find out exactly which checks are part of that method.
Are selfies, facial biometrics, liveness, and identity validation the same thing?
No. The terms describe different layers of evidence and authentication.
| Method | What does it collect? | What you can check |
|---|---|---|
| Simple selfie | Face photo | It records visual evidence, without necessarily validating identity. |
| Photo of the document | Front and/or back of the ID card | It registers the presented document, without necessarily verifying its authenticity. |
| Facial recognition | Face and reference image | Compares facial features to estimate a match. |
| liveness | Image or video of the face | Checks for signs of actual presence during capture. |
| Recognition + liveness | Document and face | Checks presence and facial match. |
| Identity validation | Document, face and other data | It can combine facial matching, document authentication, and background checks. |
This is a point where my perspective has changed along with technology. When I wrote about biometrics and facial recognitionI already pointed out that these features could improve authentication and convenience, but also demanded serious discussion about privacy and security. Today I would add another concern: knowing exactly what question each technology is answering.
A selfie answers “this image was collected”. Liveness attempts to answer “is there a real person present?”. Face matching asks “does this face match the reference?”. Documentoscopy asks “does this document show signs consistent with authenticity?”. Mixing all of this into a single expression can create a greater sense of security than the method actually offers.
How to take a selfie with your ID correctly?
The quality of the capture directly affects the analysis. Even when the process is manual, a dark, blurry, or reflective photo makes verification difficult. In facial recognition, lighting and positioning problems can also increase matching errors.
1. Use a well-lit environment.
Position yourself facing a uniform light source. Avoid photographing against a very bright window or in an environment so dark that the face loses detail.
NIST currently points to image quality as a variable capable of affecting false non-matches in facial recognition, including in situations of underexposure and overexposure.
2. Make sure your face is fully visible.
Look directly at the camera and avoid covering parts of your face with your hands, hair, or objects. If the app provides specific framing guidelines, follow them because the system may require a particular position and distance.
3. Avoid reflections in the document.
Protective plastics, screens, and direct lighting can create reflections on names, photographs, numbers, or other elements. Adjust the angle until the requested information is legible.
4. Do not cut off important edges.
When the platform requests a specific photo of the document, frame the entire indicated area. Cropping off the sides or information may prevent automatic analysis or require a new attempt.
5. Use the requested document and within the accepted conditions.
Do not assume that any document will be accepted. The process may accept RG (Brazilian National Identity Card), CIN (National Identity Card), CNH (Brazilian Driver's License), passport, or other specific types depending on the solution, country, and purpose.
6. Do not edit the images.
Filters, retouching, excessive cropping, and alterations can hinder comparison or create doubts about the capture. Use the camera and workflow indicated by the platform.
Does a selfie with identification prove identity?
Not necessarily alone.
A photograph can add evidence to the case, but the strength of that evidence depends on what happens after it is taken.
Consider two scenarios:
- simple registration: The selfie and the document are attached to the file for later reference;
- Automated verification: Algorithms compare faces, verify presence, extract data, or analyze the document itself.
In the first case, the company has further evidence, but it should not claim that a system automatically confirmed the identity if that comparison did not occur.
This distinction also appears in ZapSign's current documentation. The selfie and document photo fields can be requested separately and, in simple mode, They do not perform automatic photo validation..
How does the selfie with ID work on ZapSign?
ZapSign offers different methods because not every signature requires the same level of verification. The company can configure the workflow according to risk, document type, and the desired experience for the signer.
| Option | What are you doing | Verification level |
|---|---|---|
| selfie | It requests a photo of the signatory and records it in the process. | It does not automatically validate identity. |
| Photo of the document | Requests image of personal document. | It does not automatically validate your authenticity. |
| Selfie + document | Registers face and document in the same workflow. | Adds evidence for conference. |
| proof of life | It analyzes whether there is a real person present in the capture. | Presence |
| Facial recognition | Compares the captured face with the image on the document and includes liveness. | Presence + facial match |
| GOV+ Biometrics | It uses facial matching and data linked to compliant government verifications. | Additional identity verification |
| Identity Validation | It combines document analysis and facial matching. | More comprehensive verification |
In the current API, ZapSign explicitly differentiates these options. Selfies and document photos can only be collected, while advanced biometric methods include liveness verification, face matching, and additional validations. ZapSign documentation It also highlights the facial recognition that compares the video with the document. does not authenticate the presented document.Therefore, a validation method that includes document analysis must be chosen.
In operational terms, this avoids a common mistake: setting up facial recognition when the real concern is discovering if the document has been tampered with. These are related problems, but not identical.
The tutorial above, published on ZapSign's official channel, specifically shows how to configure authentication with selfie and document in the signature workflow.
Check out these related articles as well:
- Understand how facial recognition compares identities and what its limitations are.
- See how proof of life helps confirm the signatory's presence during authentication.
- Learn about the different levels of identity validation for digital processes.
What is the difference between facial recognition and proof of life?
Facial recognition compares features of two representations of the face. Proof of life, or liveness, attempts to verify if the capture comes from a real person present at that moment.
This matching exists because a photo of a face can be copied. The simple correspondence between two images does not, by itself, answer whether someone is physically present in front of the camera.
The article about Facial biometrics for proof of life. details this function, while the content about facial biometrics It explains how facial features are converted into technical information used for comparison.
Does facial recognition verify the authenticity of a document?
Not necessarily. In ZapSign's current implementation, facial recognition with liveness-document-match compares the captured face with the photograph presented in the document, but the documentation explicitly states that this method does not verify the authenticity of the document.
To also evaluate the document, it is necessary to use a solution of identity validation that includes this step.
This corrects a very common association:
"The face matches the photo" does not automatically mean "the document is genuine."
A fraudster might try to present a falsified document containing a matching photograph. Identity verification needs to consider what threat the company intends to block.
Is it safe to send a selfie with your ID?
It can be safe when there is a legitimate purpose, the requester is trustworthy, and the process uses adequate security and data protection controls. No selfie should be sent just because someone asked for it.
Before providing the images, please verify:
- who is requesting it;
- What is the address or application used?
- Why is the image necessary?
- which validation will be performed;
- If there is a privacy notice;
- how the data will be handled and protected;
- if the request makes sense within that operation.
HTTPS, for example, protects the transmission between browser and server, but it does not, by itself, prove that the recipient company is legitimate, nor does it determine how long the images will be stored.

The content about ZapSign security It shows how access controls, auditing, and other layers complement the authentication used during signatures.
Is a selfie with identification considered sensitive personal data under the LGPD (Brazilian General Data Protection Law)?
A person's image is personal data when it relates to someone who is identified or identifiable. It does not automatically become sensitive biometric data simply because a photograph exists.
When facial features are technically processed to identify or authenticate a person, the biometric data linked to the data subject falls into the category of sensitive personal data as provided for by the LGPD.
The difference is relevant because sensitive data has specific rules. Processing must be supported by one of the hypotheses in Article 11 and observe the general principles of data protection.
A detail closely related to this topic is found in Article 11 itself: among the legal provisions is protection against fraud and the security of the data subject in identification and authentication processes in electronic systems, respecting the conditions stipulated by law.
Therefore, saying that a company can only process biometrics "with consent" is an oversimplification. Consent is one possibility; the correct basis depends on the purpose and the specific situation.
Can the company keep the selfie forever?
The LGPD (Brazilian General Data Protection Law) does not establish a single retention period for all selfies or biometric data.
The processing must be linked to the stated purpose and applicable obligations. Articles 15 and 16 of the law address the termination of processing and the circumstances under which data may be retained subsequently.
For a company, this means defining and documenting a retention policy instead of keeping files indefinitely "because they might be useful someday."
It also makes sense to apply the principle of necessity: collect only what is appropriate and proportionate to the purpose. More information does not automatically mean more security.
What are the risks involved in taking a selfie with identification?
This method can increase the evidence of a transaction, but it does not eliminate fraud or privacy risks.
Theft of images
Selfies and documents contain information that can be exploited in scams when exposed. Therefore, secure storage, access control, and incident response remain relevant even after data capture.
Use outside of its intended purpose.
Data collected to authenticate a signature should not simply be reused for other incompatible purposes without analysis of the applicable legislation and legal basis.
False positives and false negatives
Biometric systems are not infallible. They can incorrectly reject a legitimate person or, in specific situations, associate images that should not be associated.
The ANPD and NIST also draw attention to performance differences related to technology, image quality, and demographic groups. This reinforces the need to test vendors and anticipate handling of exceptions.
Image fraud and deepfakes
The availability of photos on social media and the rise of synthetic content have increased the need to distinguish a plausible image from a real presence.
A good anti-fraud strategy doesn't just depend on "having biometrics." It combines signals compatible with the risk, such as proof of life, document verification, registration data, device, network, and other evidence.
At ZapSign, this logic also guided our product evolution. When we participated in the project that uses Open Gateway against fraudThe goal was to use signals from the telecommunications network itself to reinforce identity without forcing the legitimate user to go through yet another step. Security doesn't have to mean indiscriminate friction.
How do you choose between a simple selfie and a stronger form of validation?
The choice must be made in conjunction with the risk and consequences of the operation. This is the same logic as risk-based authentication.
| Scenario | Main question | Control to be evaluated |
|---|---|---|
| Low risk | Do we just need to add visual evidence? | Selfie or photo of the document |
| Moderate risk | We need to know if the face matches the document. | Facial recognition |
| Risk of false presentation | Do we need to confirm actual attendance? | liveness |
| Document risk | Do we also need to check the document? | Identity validation |
| High risk | Do we need to combine different signals? | Biometrics, document, registration data and context |
The mistake is placing heavier validation on all flows simply because it exists. More steps can increase abandonment and support without adding proportional value in low-risk operations.
The opposite is also bad: using a simple selfie in a process where the company believes that the document and the user have already been technically validated.
The guide to KYC This deepens the combination of risk identification, verification, and decision-making.
What happens if facial recognition fails?
First, check for simple causes: lighting, camera, framing, connection, illegible document, or incompatibility with the workflow.
In ZapSign's current documentation, advanced biometric methods allow up to three validation attempts. Upon reaching the limit without success, the signer cannot proceed until the person responsible for the flow takes action, such as restarting the attempts or changing the authentication method.
This possibility of handling exceptions is important. Legitimate individuals can fail due to technical problems and should not be automatically treated as fraudsters.
Similarly, simply releasing the operation after a repeated failure can weaken the risk policy. The process needs to establish when to retry, when to use an alternative method, and when to refer for human review.
Is a selfie with an ID considered an electronic signature?
No. It can participate in the signer's authentication, but it's only one layer of the process.
An electronic signature involves the expression of will related to the document and a set of evidence that allows a specific action to be associated with the signatory.
In a ZapSign workflow, for example, a selfie can be used in conjunction with signatory information, technical records, signed documents, and other process events.
The content about how to make electronic signature It shows how authentication, sending, and expression of will are integrated.
When a contract specifically uses facial biometrics, it's also worth understanding the legal treatment discussed in the guide on [topic]. contract with facial biometrics.
Why would a company use a selfie with an ID?
The gain appears when the collection responds to a real risk. Some common uses are registration, onboarding, relationship building, credit granting, remote acceptance, and document signing.
- More evidence: Adds information about who participated in the process.
- Remote operation: reduces reliance on in-person conferences.
- Automation: Certain checks can occur within the digital workflow itself.
- Traceability: The company is able to maintain records related to authentication.
- Step up: Verification can only be triggered when the risk justifies it.
I often come back to a very simple question when we talk about digital identity: Who's on the other side? That was the question I used when introducing the ZapSign IDSelfies, biometrics, documents, phones, and other signals may seem like separate features, but they all exist to reduce uncertainty before a decision is made.
The product challenge is figuring out how much evidence is actually needed. If the process demands too much, it increases costs and abandonment. If it demands too little, it transfers risk to the company.
What precautions should a company take when requesting selfies?
Before adding biometrics to the workflow, treat the project also as a decision about data protection, security, and user experience.
- Clearly define the purpose of the collection;
- Identify the applicable legal hypothesis;
- Reduce the data to what is necessary;
- Inform the policyholder clearly;
- Protect data during transmission and storage;
- Limit internal access;
- Record who can access the evidence;
- Define retention and disposal;
- Evaluate third parties involved in the validation;
- Test error rates and exception situations;
- Create an alternative workflow for when legitimate individuals are unable to complete the biometric verification process.
- Periodically review whether that collection is still necessary.
When the files involve contracts or highly sensitive information, the content about sensitive documents It helps to broaden the analysis to include access, encryption, and storage.
Checklist for sending a selfie with your ID.
For the user, a quick verification before sending reduces errors and scams.
| Verification | Question |
|---|---|
| Applicant | Do I recognize the company or service that placed the order? |
| Canal | Am I on the correct domain or application? |
| Goal | Do I understand why the image is necessary? |
| Face | Is it clear, well-lit, and unobstructed? |
| Document | Is it legible and of the requested type? |
| reflexes | Is there glare covering up important data? |
| Privacy | Is there information about how the data is processed? |
| Result | If validation fails, is there a legitimate support channel? |
Selfie with ID works best when each layer addresses a real risk.
A selfie with document Photos can add valuable evidence to registrations and signatures, but the level of security depends on the process behind the images. Registering photos, comparing faces, proving presence, and validating a document are all different actions.
For those signing the process, the priority is to confirm who is requesting the data and to correctly follow the capture procedure. For those designing the process, the question should be broader: what risk do we need to reduce, and what method offers sufficient evidence without making the experience unnecessarily cumbersome?
ZapSign allows you to combine different authentication methods in signature flows and choose stronger levels when the operation requires it. To apply selfie with document, facial recognition or other identity verifications in their processes, Try ZapSign and configure the method according to the risk of each document.
Frequently Asked Questions (FAQ)
Selfie with ID is a process in which a facial image and an identity document are collected to add evidence of who is performing an action. Depending on the solution, the images may simply be stored or undergo facial recognition, proof of life, document validation, and other verifications. Therefore, the name of the method alone does not indicate which validation was performed.
Use a well-lit environment, keep your face visible, avoid reflections on the document, and respect the framing indicated by the platform. Do not apply filters or edits. When the document photo is captured separately, check that the edges, photograph, and requested data are legible. Low-quality images may cause retakes or failures in automated checks.
It can be safe when the request comes from a legitimate organization and the process uses appropriate controls. Confirm the domain or application, understand the purpose of the collection, and review the privacy information. Avoid sending photos directly to unknown contacts or outside the expected flow. HTTPS protects transmission, but it does not replace storage, access, and retention controls.
Not necessarily. A simple selfie can only record visual evidence. To increase confidence, the process can add facial recognition to compare faces, liveness verification to check presence, and document validation to analyze the presented document. Before interpreting the result, confirm which checks the solution actually performed.
A person's photograph is considered personal data when it allows for their identification or makes them identifiable. When facial features are subjected to technical processing for identification or authentication, the biometric data linked to the person is considered sensitive personal data under the LGPD (Brazilian General Data Protection Law). This processing must comply with applicable legal provisions, principles, security standards, and other obligations.

Getúlio Santos is the CEO of ZapSign, a lawyer, technology enthusiast, and entrepreneur.