A strategy of KYC digital you can use a API in user registration To verify, during onboarding, whether the provided CPF (Brazilian taxpayer ID) and phone number belong to the same person. This check transforms two pieces of data that individually seem valid into an operational answer: is there a link or not? This allows for automating decisions, reducing identity fraud, and maintaining a short journey without requiring every user to go through more cumbersome authentication steps.
The difference is significant because validating the CPF (Brazilian taxpayer ID) alone does not prove that the phone number belongs to that person. official CPF lookup service It connects to the Federal Revenue Service databases and returns registration data based on the provided number. The link validation adds another question: is that number actually associated with the holder? For a risk assessment engine, this second answer changes the quality of the decision.
Summary
- CPF-phone validation adds a link check to the registration, and not just a verification of the existence of the data.
- The ideal workflow collects CPF (Brazilian individual taxpayer registration number), phone number, and consent, queries the API, and transforms a match or no match into a business rule.
- A no match doesn't necessarily mean automatic blocking: it can trigger a review or additional authentication.
- Match rate, conversion rate, latency, rejection rate, and cost per validation help to calibrate the process.
How does the API validate CPF (Brazilian individual taxpayer registration number) and phone number during user registration?
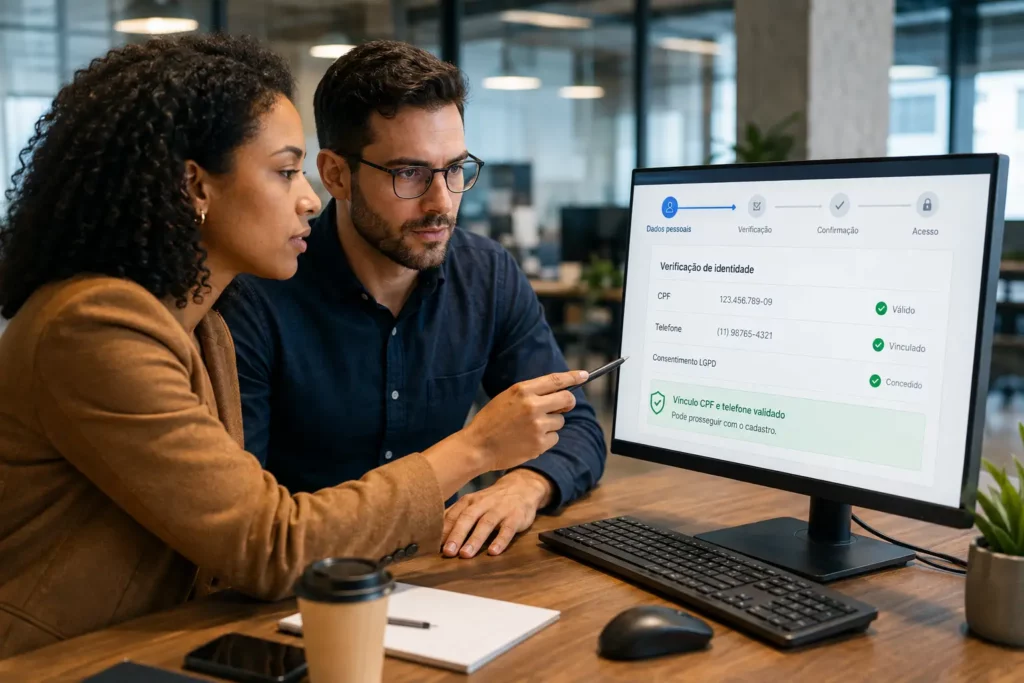
The most efficient design begins before the call. The registration process collects only the necessary data, informs the purpose of the verification, and records consent when that is the adopted basis. Then, the backend sends the CPF (Brazilian tax identification number) and phone number to the validation endpoint. ZapSign IDFor example, the CPF-telephone query was designed to directly answer whether the two pieces of data belong to the same person. It's a simple logic to integrate and, especially, simple to transform into a rule.
The pressure for this type of control is not theoretical. Data from Serasa Experian They recorded 476.060 attempted identity fraud cases during registration processes in May 2026, a 31,24% increase over May 2025. This reinforces a product choice that I consider correct: validating early costs less than discovering fraud after the account has already gained access, a limit, credit, or transactional capacity.
Matches and no-matches need to become decisions, not just technical answers.
A return of match It can release the registration, reduce the need for additional steps, or add positive evidence to other signals. A "no match," on the other hand, requires context. Automatically rejecting everything seems safe, but it can destroy conversions due to legitimate situations, such as corporate lines or registrations that require updating. The best design defines in advance when to review, when to request further proof, and when to block. That's where a... identity validation strategy It ceases to be a collection of tools and becomes operational policy.
| Result | Suggested action | Operational effect |
|---|---|---|
| Match | Approve or maintain low-friction flow. | Fewer steps for the consistent user. |
| No match with low risk | Request correction or confirmation | Avoid failing due to simple mistakes. |
| No match with high risk | Trigger additional review or authentication. | Gather more evidence before granting access. |
When I wrote about biometrics and facial recognition, my concern wasn't treating technology as an end in itself. I already argued that convenience comes with the responsibility of protecting data and privacy. This reasoning applies here: if the registration question can be answered with a CPF (Brazilian tax identification number) and phone number, it doesn't make sense to require every user to provide a selfie or document simply as a precaution.
How can we reduce fraud without turning onboarding into an interrogation?
The best treadmill is progressive. First, it performs silent, low-friction checks. If these indicate inconsistency, the system increases the difficulty. A no-match can lead to... facial recognition...documentary evidence or other mechanism compatible with the risk. This logic also appears in flows of KYC via APITechnology should select who truly needs review, instead of punishing all users with the same journey.
There is also a second problem: a telephone signal is not immutable. NIST provides guidance. Indicators such as device replacement, SIM replacement, and number portability should be considered before using the telephone network for out-of-band authentication. In Brazil, Anatel explains It states that line hijacking can occur due to number portability and informs that the procedure has adopted a second confirmation factor.
This changes the architecture of the decision. A positive link between CPF (Brazilian taxpayer ID) and phone number answers one question, but does not eliminate the need to observe the context of the line in more sensitive operations. In certain products, signals of Open Gateway or rules associated with OTP authentication They can complement the analysis. Good safety rarely depends on a single signal. It combines evidence proportionate to the risk.
LGPD requires less data collection and more discipline.
Adding controls does not authorize collecting everything. The LGPD establishes The principle of necessity limits processing to the minimum necessary for the purpose, and also provides for technical and administrative security measures against unauthorized access. In operation, this requires a clear purpose, access control, defined retention, and recording of the query result without turning the log into an indiscriminate repository of personal data.
After closely observing Estonia's digital service logic, I've come to a simple conclusion: good digitization shouldn't repeatedly ask for what the architecture can already confirm. Applied to registration, this idea favors automatic and discreet validations, with user intervention only when there's a concrete reason. Fewer forms don't mean less control. Often it means better-designed control.
What KPIs show whether the validation is working?
The most obvious indicator is the match rate, but it cannot be analyzed in isolation. A company can increase approval while simultaneously accepting more risk; or reduce fraud while decreasing the conversion of legitimate users. I prefer to treat the dashboard as a balance between security, experience, and cost. API integration It needs to be observable, and a good API documentation It helps to structure responses, errors, and events in a consistent way.
| KPI | What it reveals | Associated decision |
|---|---|---|
| Match rate | Percentage of confirmed links | Calibrate rules and database quality. |
| Failure rate | How much does the flow block? | Detect excessive stiffness. |
| Conversion | Impact of validation on onboarding. | Measure actual friction |
| Response time | User-perceived latency | Define timeout and fallback. |
| Cost per validation | Financial efficiency of the conveyor belt | Compare automation and manual review. |
It's also worth recording the reasoning behind each decision and the version of the rule applied. This avoids a scenario where legal, product, and risk teams look at the same case and arrive at different answers because no one knows which logic was in effect. In processes that later lead to contracts, integrating this history into a... electronic signature API It improves the continuity of the evidence trail and reduces rework between registration and signature.
Check out these related articles as well:
- Understand how to structure a registration validation using KYC via API.
- See how telecommunications signals can reinforce digital identity decisions.
- Learn how liveness and facial recognition can be used in higher-risk verification processes.
Validating the relationship early makes the decision simpler later.
One of the API in user registration When properly implemented, it's not just about adding a new query to onboarding. It reduces a specific uncertainty at the right moment: confirming whether a CPF (Brazilian tax identification number) and phone number belong to the same person and transforming that evidence into an automated decision. From there, the workflow can approve, review, or reinforce authentication without treating all users as suspects.
When a company combines CPF (Brazilian individual taxpayer registration number) and phone number matching, proportional rules, logs, metrics, and additional verifications only when necessary, security and conversion cease to compete for space. To bring this logic to registration with an identity-focused API, learn more about... ZapSign ID.
Frequently Asked Questions (FAQ)
These answers summarize the decisions that most commonly arise when designing a validation of the link between CPF (Brazilian taxpayer ID) and telephone number in the registration.
This means verifying if the provided number is associated with the holder of that CPF (Brazilian taxpayer ID), instead of just checking if both pieces of data exist or have a valid format. The response can feed into automatic rules for approval, review, or authentication reinforcement.
Not necessarily. A no-match is a sign of inconsistency that needs to be interpreted according to the product's risk. In lower-risk operations, it may lead to data correction. In more sensitive operations, it may trigger manual review, documentation, biometrics, or another additional mechanism.
Not in all cases. It answers a specific question about the link between two pieces of data. When the risk requires stronger proof of the user's identity or presence, the company may combine this check with documents, facial recognition, liveness, or other signals.
Ideally, the result, time, query identifier, version of the applied rule, and the resulting decision should be recorded, keeping only the data necessary for auditing and operation. The retention policy should be consistent with the purpose and internal data protection rules.
Track match rate, rejection rate, registration conversion rate, response time, cost per validation, and volume sent for review. The goal is not to maximize a single metric, but to find a measurable balance between fraud prevention, user experience, and operational efficiency.

Getúlio Santos is the CEO of ZapSign, a lawyer, technology enthusiast, and entrepreneur.